Reports
Everything you need to know about card-on-file
Card-on-file can create a seamless checkout experience for customers and improve business performance. Learn how it works and how it adds value to the shopper experience.

Card-on-file transactions lie at the heart of several types of business models, from digital subscriptions to retail, and can enable seamless customer experiences. When done right, card-on-file can lead to a higher performance, better risk management, and new cross-channel experiences for cardholders.
What is card-on-file?
Card-on-file is when you store your shopper's payment credentials (with their consent) to reuse for future payments without asking them to re-enter their card details.
Card-on-file payments generally fall into three types:
Cardholder-initiated transactions (CIT): The shopper actively selects a saved card to complete a purchase, such as a one-click checkout.
Merchant-initiated transactions (MIT): The business charges the stored card on a schedule the shopper has already agreed to, such as a subscription renewal.
Unscheduled card-on-file (UCoF): Ad-hoc or variable charges with no fixed schedule or amount, such as a ride-hailing fare or a hotel's late checkout fee.
What’s the difference between card-on-file and tokenization?
Card-on-file is about storing a shopper's payment details for reuse. Tokenization is about how you store them safely, replacing sensitive card data with a non-sensitive token. Storing card data carries PCI DSS obligations, so tokenization is usually paired with card-on-file to meet those requirements, whether you handle it directly or through a payment provider.

Use cases for card-on-file transactions
Card-on-file payments are a popular choice across many different industries, from subscriptions to mobility. Emerging industries like autonomous stores also use card-on-file to take checkout experiences to the next level.
Subscriptions
Subscriptions are standard card-on-file use cases where the cardholder provides consent to the business to bill their card periodically for a subscription. Card-on-file can also be used for additional purchases on top of the cardholder’s usual subscription package, such as transactions initiated by the cardholder.
Mobility
Mobility and micromobility transactions are usually initiated by the mobility provider’s app. The cardholder's payment details are kept on file to avoid having them re-enter their card details for every taxi, scooter, or bike ride.
Similar to mobility, food delivery apps also use card-on-file to provide cardholders with tailored customer experiences.
Travel and hospitality
In the travel and hospitality sector, card details are usually stored on-file during booking for pre check-in costs such as no-show charges or partial charges following conditions of the accommodation. At check-in, the merchant also stores the card-on-file to enable incidental charges, such as those from restaurant visits or damages.
Autonomous stores
The core premise in an autonomous store is the absence of a checkout. AI-driven store solutions detect the shoppers’ interactions and charge the total amounts when they walk out of the store. Card-on-file payments are then used to complete the payment during the walk out phase.
Unified commerce retail
Businesses leveraging unified commerce can collect card details in one channel and use them in another to complete payments and make refunds.
Buy Now, Pay Later providers
Buy Now, Pay Later (BNPL) providers can offer their customers the option to pay off their installments using a card-on-file that is charged periodically by the BNPL provider.

How does card-on-file work?
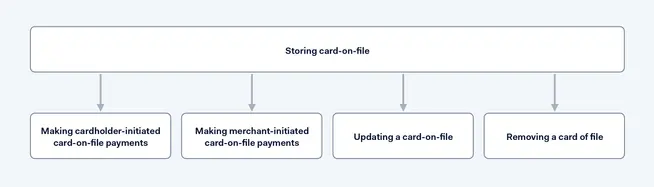
Leveraging card-on-file involves different processes starting with storing the card-on-file, then making cardholder-initiated card-on-file payments or merchant-initiated card-on-file payments, updating the card-on-file, and possibly removing it.
Storing the card-on-file
Storing a card-on-file requires the cardholder's consent and can be done by:
Making a purchase and agreeing to store the card-on-file for future transactions.
Verifying the account through a zero-amount transaction.
Completing an in-person payment. This is commonly used in unified commerce, where a card stored on file in store can be used for online purchases.
At Adyen, we take responsibility for confirming the shoppers consent to storing a card-on-file for future purchases to the issuing bank.
FAQ: What needs to be included in the card-on-file storage agreement that the cardholder must consent to?
Information about the transaction, including a description of the goods and the total amount that will be billed.
Information about the business, including its location and contact details.
A shortened version of the stored credential (such as the last four digits of a credit card).
Information on how the stored credential will be used and the expiry date of the agreement if applicable.
Instructions on how the cardholder can cancel the agreement.
FAQ: Can the business store the card-on-file themselves? Or do they need to use a payment provider for this?
Payment card data storage comes along with PCI-DSS security requirements If the business wants to store the data it needs to be compliant and audited. Adyen is fully PCI level 1 compliant and can store payment card data securely on behalf of merchants.
FAQ: Can the CVV/CVC code be stored?
Due to PCI regulations, neither the business nor the acquirer can store the CVV/CVC code on file.
Cardholder-initiated card-on-file payments
A cardholder-initiated card-on-file transaction is when the customer selects the previously stored card data to pay for goods or services without having to enter their card details again. It’s commonly used in a one-click card-on-file transaction and often needs to be authenticated with 3D Secure technology.
Merchant-initiated card-on-file payments
A merchant-initiated transaction is when the cardholder consents to the merchant taking the money from their account. These transactions are linked to the cardholder-initiated transaction where the agreement was initially set up.
Merchant-initiated transactions include:
Subscriptions
Recurring transactions at scheduled intervals using a card-on-file. Commonly used for streaming service subscriptions or recurring utility payments.
Unscheduled card-on-file transactions
Transactions that don’t occur at a scheduled/recurring date but are triggered by an event. Commonly used for account top up transactions.
Installments
When a single purchase of goods/services is split up into several transactions scheduled at pre-agreed dates.
Industry specific merchant-initiated transactions
No-shows: Commonly charged by hotels in case a customer fails to show up to a reservation.
Delayed charges: Transactions used to process supplementary charges after the original services have been delivered. These are delayed as the charges aren’t evident at the point when the original transaction is processed.
Resubmissions: Used when the original authorisation was declined due to insufficient funds.
FAQ: Does the customer need to be verified to use their card-on-file details?
During a cardholder-initiated card-on-file transaction the business needs to verify the identity of the cardholder. In some regions it’s required to use 3D Secure for strong customer authentication (SCA) when the purchase amount is above a certain threshold.
Alternatively, the merchant can collect the 3-digit CVC/CVV code from the cardholder as an additional verification during the checkout.
For merchant-initiated card-on-file transactions there is no need to verify the cardholder’s identity.
FAQ: Can stored credentials be used across different sales channels?
It all depends on the agreement between the merchant and the cardholder. If the card-on-file is to be used over different channels, it needs to be part of the agreement. If the card-on-file was stored following an in-store payment and the agreement states that the details can be used for future subscription charges or for future ecommerce one-click charges, then it’s possible to use them across channels.

Updating a card-on-file
Card-on-file information will probably need to be updated at some point as cards expire or changes are made to the PAN. This results in a lot of friction as transactions are declined and cardholders are asked to update the information.
With Adyen, any update to the card is automatically picked up, leading to reduced declines and seamless cardholder experiences.
FAQ: What happens when a customer wants to upgrade their subscription from a standard to a premium plan? Does the business need to verify the customer’s identity again?
Changes to the card-on-file agreement need to have the cardholders consent. Therefore, the cardholder needs to be verified again.
Removing a card-on-file
Storing a card-on-file requires establishing the terms of the agreement, including cancellation and refund policies. If the time-period specified in the agreement ends or the cardholder wants to cancel the agreement, the card-on-file can’t be used to process the transaction and the details need to be removed.
How Adyen approaches card-on-file
Adyen is a global payments platform used by businesses including Uber, Spotify, and Booking.com, processing payments across online and in-store channels through a single infrastructure. Here's what you can expect if you partner with us:
Reduce PCI scope with tokenization
Storing card data yourself means taking on PCI DSS compliance and the audit burden that comes with it. Adyen replaces the primary account number with a secure token at the point of storage, through both our own tokenization and native integration with the card schemes' tokenization services (Visa's Token Service, Mastercard's Digital Enablement Service, JCB, and American Express). Because raw card data never sits in your environment, your PCI DSS scope shrinks significantly.
Protect authorisation rates with real-time account updates
A stored card is only useful if it keeps authorising. Real-Time Account Updater connects directly with the card networks to catch expired, lost, or reissued cards before they cause a decline, which is what stops routine card reissuance turning into lost subscription revenue. Adyen's Total Cost of Payments report puts this at $1.08 billion saved across the top 100 businesses on the platform over a 12-month period, through account updates alone.
Recover revenue with smart retry logic
For payments that are refused or charged back but still have a real chance of succeeding, such as a temporary insufficient-funds decline, Auto Rescue schedules retries at the times most likely to work, rather than retrying blindly or giving up after a single attempt. And because not every transaction benefits equally from a network token versus the underlying card number, network token optimisation decides which to use on a transaction-by-transaction basis, balancing authorisation rate against scheme cost.
Handle compliance with automated lifecycle tracking
Recurring and one-click card-on-file payments carry their own scheme-level requirements: Transactions need the right indicators to show they're linked back to the original authenticated payment, and cardholder-initiated and merchant-initiated transactions need to be labelled correctly. Adyen tracks this lifecycle automatically, so the right scheme references travel with every transaction without your team needing to manage the detail manually.