Article
Boost your webhook security: set up OAuth 2.0
Discover how to secure payment webhooks using OAuth 2.0 and short-lived tokens. Follow our step-by-step guide to configure your IdP and webhook endpoints.

We use Open Authorization (OAuth 2.0) for payment webhooks. It’s a more secure way to protect your data, giving you temporary token access to secure your sensitive payment events. It’s one of the many ways we look out for our customers’ security.
What is OAuth 2.0?
OAuth 2.0 is an open protocol that enables secure authorization across different applications. It’s distinct among other protocols because it doesn’t share any direct credentials. Your application will exchange credentials for a temporary access token instead.
The Monetary Authority of Singapore expects that modern financial institutions will use a vigilant Zero-Trust Architecture approach, where all transactions require verification. Here’s where short-lived tokens can provide an extra layer of security. Key benefits:
Reduced exposure: Access tokens typically expire in a few hours, so it limits the window of opportunity for an attacker if they intercept your token.
Layered defense: Integrating OAuth 2.0 with HMAC provides a more secure configuration to accept and validate webhook contents.
Standardized protocol: OAuth 2.0 is an open protocol, meaning your team likely already uses it for other integrations, reducing the learning curve. Note: OAuth 2.0 support is currently available only for the type.
Here’s how it works
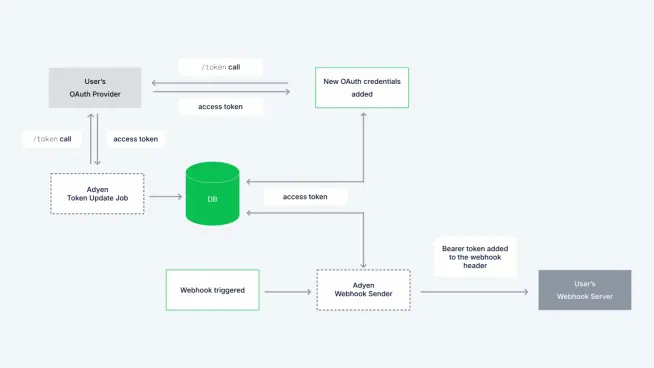
With an OAuth 2.0 implementation, Adyen acts as an OAuth client and requests an access token from your system to authorize the delivery of webhook events.
Adyen requests a token from your OAuth 2.0 Identity Provider's authorization server.
Your authorization server validates the credentials and issues a token.
Adyen sends this access token in the header of each webhook event, allowing you to authenticate the request at your endpoint.
Here’s how to set up OAuth 2.0
Configuring OAuth 2.0 is a two-part process: first, within your own Identity Provider (IdP), and second within the Adyen Customer Area. Step 1: Configure your Identity Provider (IdP) You need to create an application in your IdP’s developer console that Adyen can authenticate against. To do this:
Create a new application/client in your IdP.
Generate the required credentials: Client ID, Client Secret, and Token URL.
Define your scope (optional, but recommended for granular control).
Configuration requirement: Ensure the Time-to-Live (TTL) setting for your access tokens is set to a minimum of 3,599 seconds. This allows Adyen's background process to efficiently update with no service interruption. Step 2: Update your webhook settings in the customer area
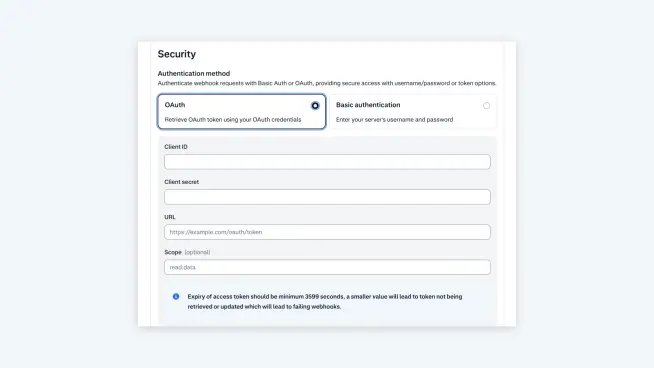
Log in to the customer area and navigate to Developers > Webhooks.
Select the standard webhook you wish to edit or add a new one. Under Security, select OAuth.
Enter the credentials you generated in Step 1 (Client ID, Client Secret, URL, and Scope).
Click Save configuration and verify your connection.
Tips for webhook security best practices
Protect your client secret: The client secret must be protected. To stop potential misuse, it should never be embedded in client-side code.
Principle of least privilege for scopes: We strongly encourage following the principle of least privilege. Tokens should have the least permissions possible. Scopes (which are required for security purposes) define how and to what extent the system can access resources.
Rotate credentials: Static credentials are a risk. Even with OAuth, we recommend periodically rotating the client secret stored in the customer area. This proactive measure ensures that even if a secret was inadvertently logged or exposed on your side, attackers can't use it indefinitely.
What are the next steps?
OAuth 2.0 has been available for all since the end of Q2 2026. Keep an eye on for updates, and subscribe to our . (Sam’s note: has this been implemented? OAuth 2.0 should be available now.) Important Note: Although basic authentication is still supported, we strongly recommend migrating to OAuth 2.0. It's the more secure standard, and we plan to deprecate basic authentication in the long term. Ready to upgrade? Don't wait for the deprecation deadline. today by switching to OAuth 2.0. It significantly reduces risk and secures your integration.