Article
PSD3: What you need to know
New proposals for PSD3 are being put into place. Discover what this means and how it benefits the payments industry.
Key changes:
Payment Services Directive 3 (PSD3) is an updated version of Payment Services Directive 2 (PSD2) and provides rules on the efficiency and security of electronic/digital payments and financial services in the EU. It aims to improve competition and innovation in the financial industry.
PSD3 sets out more extensive Strong Customer Authentication (SCA) regulations and stricter rules on access to payment systems and account information.
PSD3 aims to protect consumers’ rights and personal information while improving competition in the payments industry.
The new proposals also include a new Payment Services Regulation (PSR) to improve consumer protection. This will be directly applicable to EU member states.
Timeline: There is yet to be a clear timeline for implementing PSD3 and PSR. The finalized versions might be accessible by late 2024. The member states usually receive an 18-month transition period, suggesting that PSD3 and PSR could take effect around 2026.
Since introducing the previous Payment Services Directive (PSD), the EU payment services market has experienced significant transformations. This is due to the rise of electronic payments and the entry of new providers offering open banking services.
The main objective of the last Payment Services Directive (PSD2) was to ensure a level playing field between existing and new providers of card, internet, and mobile payments.
Due to developments in the market, the rules and regulations around payments were calling for an update. On June 28, the European Commission put forward proposals to bring payments and the wider financial sector further into the digital age. These proposals will amend and modernize PSD2, which will become PSD3, and introduce a Payment Services Regulation (PSR).
This blog provides a high-level overview of the European Commission’s Payment Services Directive 3 (PSD3) proposals, how they compare to PSD2, and how this will impact the payments industry.
What is PSD3?
PSD3 is an EU Directive that provides rules for the authorization and supervision of non-bank payment service providers (PSPs) in the EU. The PSD3 aims to protect consumers’ rights and personal information while improving competition in the payments industry. This will empower consumers to securely share their data and contribute to a broader range of innovative financial products and services. Since it’s a directive, the PSD3 rules need to be transposed into the national laws of the various EU Member States.
What is PSR?
PSR is an EU Regulation that directly applies to the EU Member States once adopted and entered into force. The PSR will be directly applicable without the need for transposition by member states at a national level. This contributes to a uniform and consistent implementation across the entire EU. The PSR aims to improve consumer protection, an area in which consistency of rules is crucial.
PSD2 vs PSD3
PSD3 will cover a more extensive scope than PSD2. This makes it more suitable for today’s payments landscape given the uneven implementation of rules that could encourage regulatory arbitrage. It covers most parts of PSD2, such as transparency, liability, and open banking. However, PSD3 sets out more extensive Strong Customer Authentication (SCA) regulations and stricter rules on access to payment systems and account information compared to PSD2. This plays a pivotal role in safeguarding payment transactions and counteracting payments fraud.
Learn more about how PSD2 and SCA have been interacting up until now.
PSD3's impact on the payments industry
The changes regarding Strong Customer Authentication (SCA) and access to payment systems and account information will affect the payments industry. Let's look at these changes and how they will make a difference.
Strong Customer Authentication
The PSD3 changes regarding SCA will contribute to safer buying experiences. There will be new rules around data sharing, fraud prevention, authentication, transactions, and accessibility.
Data Businesses will need to share more data with issuers, allowing them to monitor environmental and behavioral characteristics such as user location, transaction time, devices used, spending habits, transaction history, session data, and device IP. As a result, they can increase approval rates by better determining which transactions to approve and which to decline. Payment schemes and PSPs will also be allowed to process personal data for fraud prevention without explicit user consent under the General Data Protection Regulation (GDPR). This only applies if they use the data to prevent fraud.
Fraud The new proposals also suggest a liability shift in terms of fraud. Schemes, technical service providers (such as wallet providers), and payment gateways will be liable for fraud if they fail to apply SCA. This protects payers from technical malfunctions and encourages providers to maintain a high quality of service.
Issuers will also be liable when spoofing fraud occurs. This is when a fraudster impersonates a bank’s employee to make the user authenticate the payment. If the payer acts fraudulently or with gross negligence, they will remain liable.
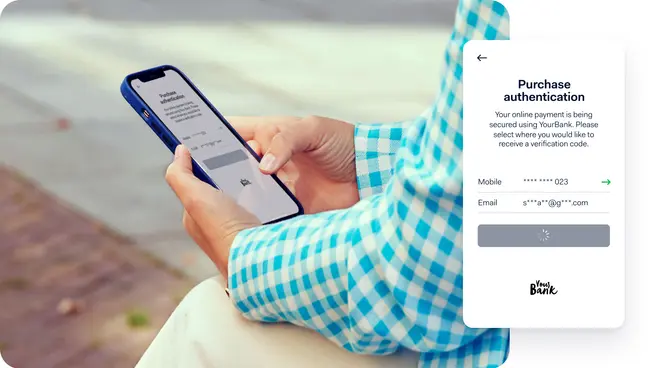
Authentication PSD2 required SCA factors to belong to two categories out of the following three: knowledge, possession, and inherence. With PSD3, using two of the same categories, like token and SMS OTP or even two passwords, is possible.
SCA delegation by issuers to third parties, such as Apple Pay, is now qualified as outsourcing and needs to comply with outsourcing rules to authenticate the cardholder. Adyen anticipated that outsourcing would be regulated and created a Delegated Authentication solution that allows us not to outsource to a third party but instead do the authentication ourselves. So issuers can delegate SCA to us.
Exemptions Merchant-initiated transactions (MIT), such as subscriptions, are now excluded from SCA. Only the first transaction requires SCA. MITs will have the same 8-week unconditional refund right (‘no question asked’) that you find in SEPA Direct Debits.
Similarly, card-based mail orders and telephone orders, also called MOTO transactions, don’t need to be authenticated with SCA. This exemption will greatly benefit sectors such as the travel industry.
Regarding tokenization, SCA is only required if the cardholder initiates the transaction, for instance, during a card-on-file transaction or when a cardholder initially enrolls their card in a digital wallet.
Accessibility SCA must now be accessible for vulnerable customers such as the elderly, people with disabilities, and non-digitally savvy consumers by providing authentication methods that don’t rely solely on smartphones.
Access to payment systems and account information
The PSR will introduce changes to the existing Open Banking framework that will remove obstacles to providing open banking services and ultimately increase uptime for banking and financial services.
Payment Initiation Service Providers (PISPs) and Account Information Service Providers (AISPs) will be allowed to build custom interfaces that connect to banks and other financial institutions.
Banks and financial institutions will have to share more information about their API performance by publishing quarterly statistics on interface availability and performance, creating a higher level of transparency. This gives businesses more accurate insights into the payment systems, helping them to make informed decisions about which partner they want to choose for their payment processing needs.
In case of bank downtime or disruptions, banks need to allow third parties (AISPs and PISPs) to use their own banking interfaces, leading to more efficient payment processes for digital businesses and their customers. Following applicable civil law, businesses also retain the right to claim damages for losses incurred.
Banks are required to provide customers with a permission dashboard. This dashboard allows customers to continuously monitor and manage permissions granted to AISPs conveniently.
What’s next?
The PSD3 and PSR proposals ensure consumers can continue safely and securely making electronic payments and transactions in the EU, domestically or cross-border, in euro and non-euro. It aims to provide a greater choice of payment service providers while safeguarding customers.
At Adyen, we're working with regulators and card schemes to ensure everything is ready for PSD3. At the moment, there are no further actions required. We'll keep you up to date on the latest developments of the regulations via email and system messages to ensure an optimal experience.
There is yet to be a clear timeline for implementing PSD3 and PSR. The European Parliament and European Council will review the proposed changes. The member states usually receive an 18-month transition period, suggesting that PSD3 and PSR could take effect around 2026. If you want to find more details, visit the official documents here.
Learn more about how to balance convenience with security through better authentication here.
What’s changing with PSD3 / PSR
With the substance of the rules now settled, here's what you need to know across six key areas, from authentication and fraud liability through to open banking, scheme fees, licensing, and currency conversion.
1. Strong customer authentication (SCA): Mostly the same although exemptions will tighten
In essence, SCA isn’t going anywhere. You’ll still need two of three categories (something you know, something you have, something you are) to authenticate a payment. The only key difference is that two biometric checks can now fulfill the requirement as well as two separate categories. Merchant-initiated transactions for recurring billing also stay as they are: One authentication check at setup, none on renewal, and no unconditional refund right for consumers (unlike a direct debit payment).
The main differences in SCA are found in exemptions:
The contactless exemption could rise from €50 across the EU (it’s already £100 in the UK).
Exemptions around mail order and telephone (MOTO) payments will continue but regulation will be tightened.
The transaction risk analysis exemption remains but its qualifying conditions could change.
PSD3 passkeys typically pair a device the customer holds with a biometric check on that device, which fits the two-category model SCA already uses. The new allowance for two biometric checks widens the options further. Whether a specific passkey flow qualifies as SCA will depend on the EBA’s technical standards. In the meantime, Adyen Authenticate supports Google Secure Payment Authentication, Mastercard Payment Passkeys, and Visa Payment Passkeys alongside 3DS, routing each transaction to the method most likely to succeed.
2. Fraud liability is more evenly spread across the payment ecosystem
PSD3 and PSR reshape who's liable when fraud happens, shifting more of the burden away from customers and spreading it across banks, schemes, and technical providers. For example:
Impersonation and spoofing fraud: PSR introduces an automatic refund right for some cases of impersonation or spoofing fraud, such as impersonating a bank employee to tricking a customer into authorizing a payment. In this case, liability sits with the customer’s bank (provided the customer hasn't acted fraudulently or with gross negligence).
Liability across the payment chain:
Issuing banks can seek to recoup losses from acquirers, which increases the likelihood of chargebacks reaching businesses further down the chain.
Consequently, acquirers now face their own obligation to monitor transactions for fraud risk. In practice, that's likely to mean acquirers asking businesses to share more transaction data to support the assessment.
Card schemes, technical service providers such as wallet providers, and payment gateways can also be held liable if they fail to apply SCA correctly, protecting payers from technical failures and giving providers a clear incentive to maintain consistent quality of service.
Verification of Payee: All bank-to-bank credit transfers must now be checked in advance to confirm the payee's name matches their account details. This is most relevant to businesses running payout flows such as platforms, marketplaces, investment platforms, and insurers.
PSD3 Transaction monitoring: PSR requires PSPs to run risk-based monitoring of transactions and links a failure to monitor to refund outcomes. It also gives PSPs a clearer legal basis to share specified fraud-related data with each other, within GDPR safeguards. The technical detail will come from the EBA’s standards, so expect acquirers to ask businesses for richer transaction data over time.
3. Open banking interfaces to be more open and reliable, improving trust and encouraging wider adoption
PSR's objective is to make the open banking ecosystem more open and transparent.
To get there, banks must build a reliable, dedicated connection that lets payment and account information providers act on a customer's behalf and publish how well that connection performs every quarter. If the connection goes down or works badly, providers can fall back on the bank's normal online banking system instead, so payments keep going through. If a business loses money because of a failure, it can claim damages under the usual civil law rules.
Banks are also required to offer consent dashboards, clearly showing customers which third parties have access to their account data, along with the ability to revoke that access at any time.
This gives customers real control over their data and builds trust, while more reliable interfaces make pay by bank a viable, cheaper alternative to card payments.
4. More transparency around schemes fees, allowing acquirers to optimize costs on behalf of businesses
PSR strengthens transparency around card payment costs by requiring card scheme operators and processing entities to clearly define, unbundle, and disclose all fees charged to acquirers in a standardized, comparable format.
Scheme fees must be broken down granularly, split into mandatory fees, fees linked to specific behaviors or technology use, and fees for optional services, with explicit breakdowns by card category, sales channel, volume, and geography.
Card schemes and processing entities must also give at least six months' notice of any fee changes before they take effect, and maintain a single, public EU repository detailing their scheme rules and fee schedules.
These transparency rules will be further detailed in a Delegated Regulation to be adopted by the European Commission, expected during 2027.
These updates are expected to give acquirers the insight to spot unexpected behavioral penalties, optimize payment routing, and bring down card acceptance costs overall. For example, Adyen's platform helps businesses analyze scheme cost structures and automatically optimize transaction routing across domestic and international networks.
Learn more about how we can help you optimize your payment costs.
5. Payment and e-money institutions to be merged under a single, tighter regime
PSD2 regulates payment institutions and e-money institutions (EMIs) under separate licenses, allowing e-money institutions to issue e-money and perform payment services, while payment institutions are only allowed to perform payment services.
PSD3 merges these licenses under a single regime for payment institutions, with stronger requirements for payment institutions that issue e-money. This means that existing e-money and payment institutions must engage with supervisors to ensure compliance with the new authorization requirements.
6. Cross-border transfers and currency conversion fees to be disclosed upfront
The PSD3 impact on cross-border fund transfers comes mainly through PSR, which requires PSPs to clearly disclose all currency conversion charges on credit transfers and money remittance transactions. The charge must be shown as a percentage mark-up over the European Central Bank’s official FX rate before the transaction is initiated. Checkout flows and receipts must be updated to show these costs transparently, and the rules also tighten how Dynamic Currency Conversion charges are displayed at checkout.
Spotlight on platforms and marketplaces
Platforms and marketplaces that operate without a payments license may need to reassess their regulatory operating model to stay compliant with PSR. Many platforms and marketplaces rely on the commercial agent exemption under PSD2 to offer payment services. However, under PSR, it is not certain that the commercial agent exemption will remain available for these business models.
PSR restates the two cumulative conditions for the exemption that applied under PSD2:
Only one side of the deal: The agreement must clearly state that the agent (the platform or marketplace) works for either the buyer or the seller. Never both at once.
Real decision-making power: The agent must be able to negotiate or conclude the sale, not just process a payment for a sale that's already been made. For example, a travel agent who negotiates rates and puts together a package directly with hotels and airlines is exercising decision-making power over the deal.
While these conditions for the exemption existed under PSD2, PSD2 was a Directive meaning each EU Member State took its own approach to implementing it into its national law. The result was different applications of the commercial agent exemption in practice. PSR’s stated aim is to bring more consistency to the application of the exemption across the EU by formalizing the conditions in a directly applicable Regulation. Additionally, PSR mandates the EBA to develop guidelines for national regulators on the application of the exemption.
It’s not yet clear whether the commercial agent exemption will continue to be available for platforms and marketplaces that have relied on it under PSD2. Once the EBA guidelines on the exemption are published, platforms and marketplaces will need to assess their business models and determine if the exemption is still applicable.
Banking-as-a-service PSD3 changes for platforms
Banking-as-a-service changes arrive mainly through licensing, because e-money and payment institutions move under a single regime and existing institutions must apply under the new authorization requirements. Safeguarding and governance rules are being aligned too. If you embed financial services through a banking-as-a-service partner, ask how it plans to re-authorize and what that means for the services you rely on.
How Adyen can help platforms and marketplaces stay compliant
Unless you meet both the conditions set out above, you must now become licensed as a payment institution, or work with a provider that already is, such as Adyen.
Our dedicated solution, Adyen for Platforms, lets you embed payments directly into your platform or marketplace. And, because we're a bank, we can hold buyer and seller funds directly in dedicated bank accounts under our own license. That means one licensed platform for both payment processing and marketplace fund handling.
PSD3 compliance checklist for merchants
Even with formal adoption still pending, there are a few steps businesses can take now to ensure they’re ready when the Official Journal is published and the countdown begins:
Check your exemptions: Map what share of transaction volume currently relies on an SCA exemption. This will determine how much any future change will impact your checkout flow.
Platforms and marketplaces assess your licensing requirements: Reassess your business model in light of the updated conditions for the commercial agent exemption once the EBA guidelines are published. And, if necessary, decide whether to become licensed or work with a vendor that is.
Get your voice heard: The EBA's regulatory technical standards haven't been written yet so now’s a good moment to engage (either directly or through industry bodies) to ensure the details work in your businesses’ favor.
If you'd like more information about how Adyen helps ensure its customers remain compliant with all major global regulations, get in touch.
PSD3 FAQs
Yes. Besides the text of PSD3 and PSR themselves, the rules will be defined in further detail by Regulatory Technical Standards (RTS) and Guidelines to be developed by the EBA. These so-called “Level 2” and “Level 3” measures will flesh out the regulatory requirements in areas such as SCA, anti-fraud transaction monitoring mechanisms, and Open Banking.